YOUR TOOLS. CONTROLLED AUTONOMY. MDR EVOLVED.
The Atlas Platform
MDR that moves first. Agentic AI and human experts on your side, 24/7.
Deploy Atlas for 30 Days FreeConnects to any signal across any vendor stack and powers adaptive AI Operatives that expose, detect, and neutralize cyberattacks.
Atlas Operations CenterSee what our SOC sees, review investigations, and see how we are protecting your business.
Technology IntegrationsAtlas connects to any signal across your current security tools. Whatever you're running, we're running with you.
Extend your team with immediate expertise, hands-on remediation, and the human accountability layer that boards, regulators, and cyber insurers require.
Threat Response UnitProactive threat intelligence, original threat research and a world-class team of seasoned industry veterans.
Response and RemediationPairs machine-speed containment with human judgment, delivering full threat response that's policy-bounded, reversible, and explainable.
MDR that moves first, multi-signal attack surface coverage, and 24/7 Elite threat hunters working as one continuous security program across any vendor stack.
Get unlimited Incident Response with threat suppression guarantee- anytime, anywhere.
Atlas Preempt deploys AI Operatives to continuously validate attack paths exposing attacker targets of opportunity before they take advantage.
Flexible MDR pricing and packages that fit your unique security requirements.
Entry level foundational MDR coverage
Comprehensive Next Level eSentire MDR
Next Level eSentire MDR with Cyber Risk Advisors to continuously advance your security program
Stop ransomware before it spreads.
Identity ResponseStop identity-based cyberattacks.
Zero Day AttacksDetect and respond to zero-day exploits.
Cybersecurity ComplianceMeet regulatory compliance mandates.
Third-Party RiskDefend third-party and supply chain risk.
Cloud MisconfigurationEnd misconfigurations and policy violations.
Cyber RiskAdopt a risk-based security approach.
Mid-Market SecurityMid-market security essentials to prioritize.
Sensitive Data SecurityProtect your most sensitive data.
Cyber InsuranceMeet insurability requirements with MDR.
Cyber Threat IntelligenceOperationalize cyber threat intelligence.
Security LeadershipBuild a proven security program.
On September 6th, 2026, N-able disclosed and patched three critical and high-severity vulnerabilities in the N-central RMM platform, with one flaw confirmed exploited in the wild. The…
2026-09-02 Update: On September 1st, 2026, PaperCut Software released Emergency Patch (Release 3) for customers with Internet-facing PaperCut NG/MF Application Servers that are…
eSentire is a leader in Controlled Autonomy SecOps, protecting 2,000+ organizations across 35+ industries around the world. Founded in 2001, the company’s Controlled Autonomy SecOps operating model pairs agentic AI operatives with engineered human-judgment controls, delivering expert-depth security outcomes at machine speed without ceding accountability to opaque automation.
About Us Leadership Careers Event Calendar → Newsroom → Aston Villa Football Club →We provide sophisticated cybersecurity solutions for Managed Security Service Providers (MSSPs), Managed Service Providers (MSPs), and Value-Added Resellers (VARs). Find out why you should partner with eSentire, the Authority in Managed Detection and Response, today.
Search our site
Multi-Signal MDR with 300+ technology integrations to support your existing investments.
24/7 SOC-as-a-Service with unlimited threat hunting and incident handling.
We offer three flexible MDR pricing packages that can be customized to your unique needs.
The latest security advisories, blogs, reports, industry publications and webinars published by TRU.
Compare eSentire to other Managed Detection and Response vendors to see how we stack up against the competition.
See why 2000+ organizations globally have chosen eSentire for their MDR Solution.
MDR that moves first. Agentic AI and human experts on your side, 24/7.
Deploy Atlas for 30 Days FreeControlled Autonomy SecOps
See Atlas in Action
Every Integration
Preempt, Detect, Respond
Atlas vs. Others
Resources
Atlas FAQ
Atlas combines real-world attacker intelligence, elite agentic AI operatives, and human expertise on the loop. MDR has evolved to move first, delivering the speed, context, and precision needed to stay ahead of adversaries.

95% tier-3 analyst validation alignment
TCP disruption, host isolation, user suspension
200+ threat protections added daily
Hundreds of real-world tools and agentic hacking tools
You're managing dozens of tools that were never built to talk to each other. Whatever you're running, we're running with you. Atlas meets your stack where it is.
Agentic AI operatives on offense uncover exposures before attackers can. Offensive and defensive findings forge the intelligence that drives MDR. Response moves at machine speed with controlled autonomy, before damage is done. Continuous feedback across the entire customer base.
Connect your stack. See real threats in your environment, not a demo.
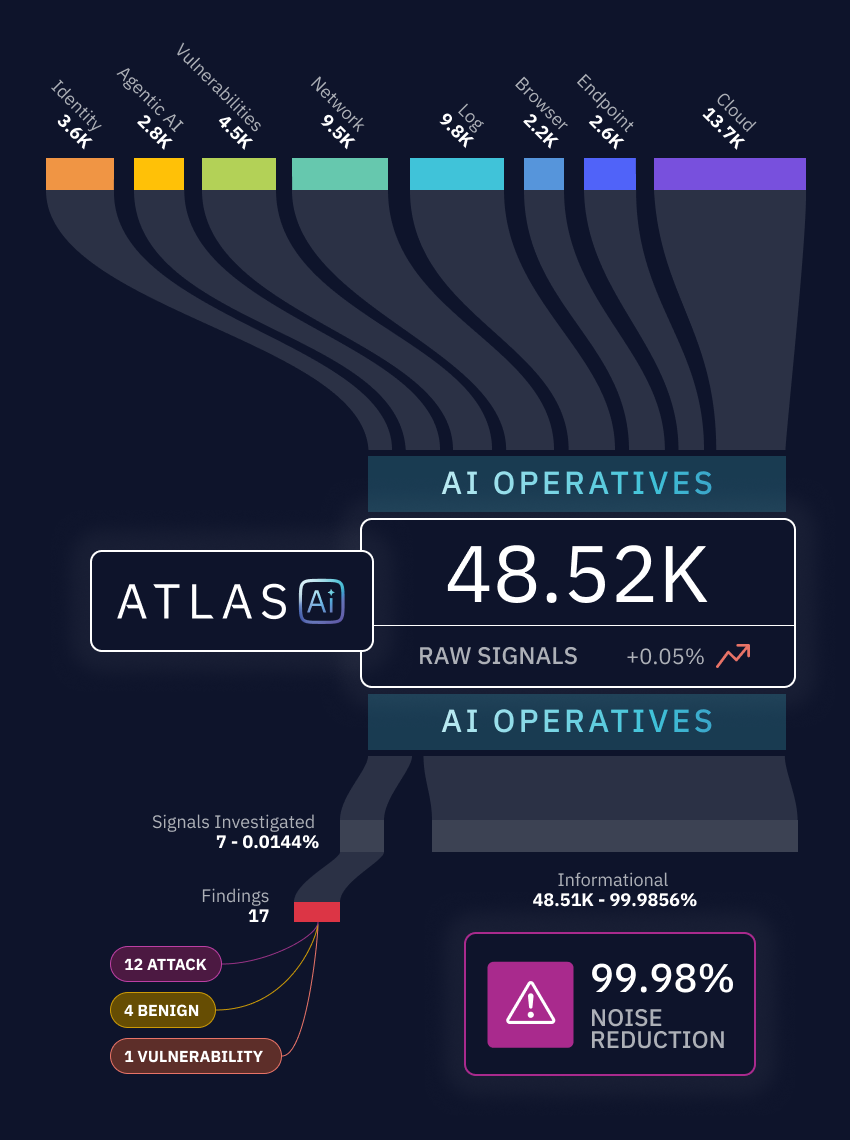
Atlas is eSentire's Controlled Autonomy SecOps platform. It connects to your entire security stack, correlates signals across endpoints, network, identity, email, cloud, SaaS, and more. Leveraging AI operatives, Atlas preempts exposures, detects threat actor activity, and disrupts cyberattacks before they land.
Most MDR and XDR platforms wait for something bad to happen, then respond. Atlas starts with offense. It tests your environment the way a real attacker would, feeds those findings into detection, and uses response actions to immediately shut down the attackers all in a single platform. That's a fundamentally different operating model.
Atlas investigates, correlates, and recommends, but no host gets isolated, no action gets taken, and no response gets executed without a SOC analyst reviewing and approving it first. No exceptions. AI handles the volume and speed. Humans ensure accuracy, context, and judgment.
Atlas supports the integrations that matter to you, across many signal sources. It's included as part of your eSentire service with no additional setup. Review our integrations or contact us if you would like information on a specific integration.
No. Atlas is the platform that powers your eSentire service. It's not an add-on or upsell — it's the engine underneath everything we deliver.
Atlas ingests telemetry from your existing stack through pre-built integrations, which means time-to-value is measured in hours, not days. Your environment reaps the benefits of eSentire's Controlled Autonomy approach and the refined protections delivered across our entire customer base.
Guardrails catch known patterns; novel attacks need human adjudication. Other vendors sell you a dashboard and leave the monitoring to your team. Atlas AIDR includes our 24/7 SOC and Elite Threat Hunters because AIDR without a SOC is like EDR without MDR. We don't just give you a tool to run—we provide a managed outcome, watching the AI supply chain, identifying supply-chain drift, and investigating anomalous spend as a compromise signal, 24/7.
Start today and see how Atlas delivers faster than the attacker.